
CRA reporting system FAQ
When do the CRA reporting obligations begin?
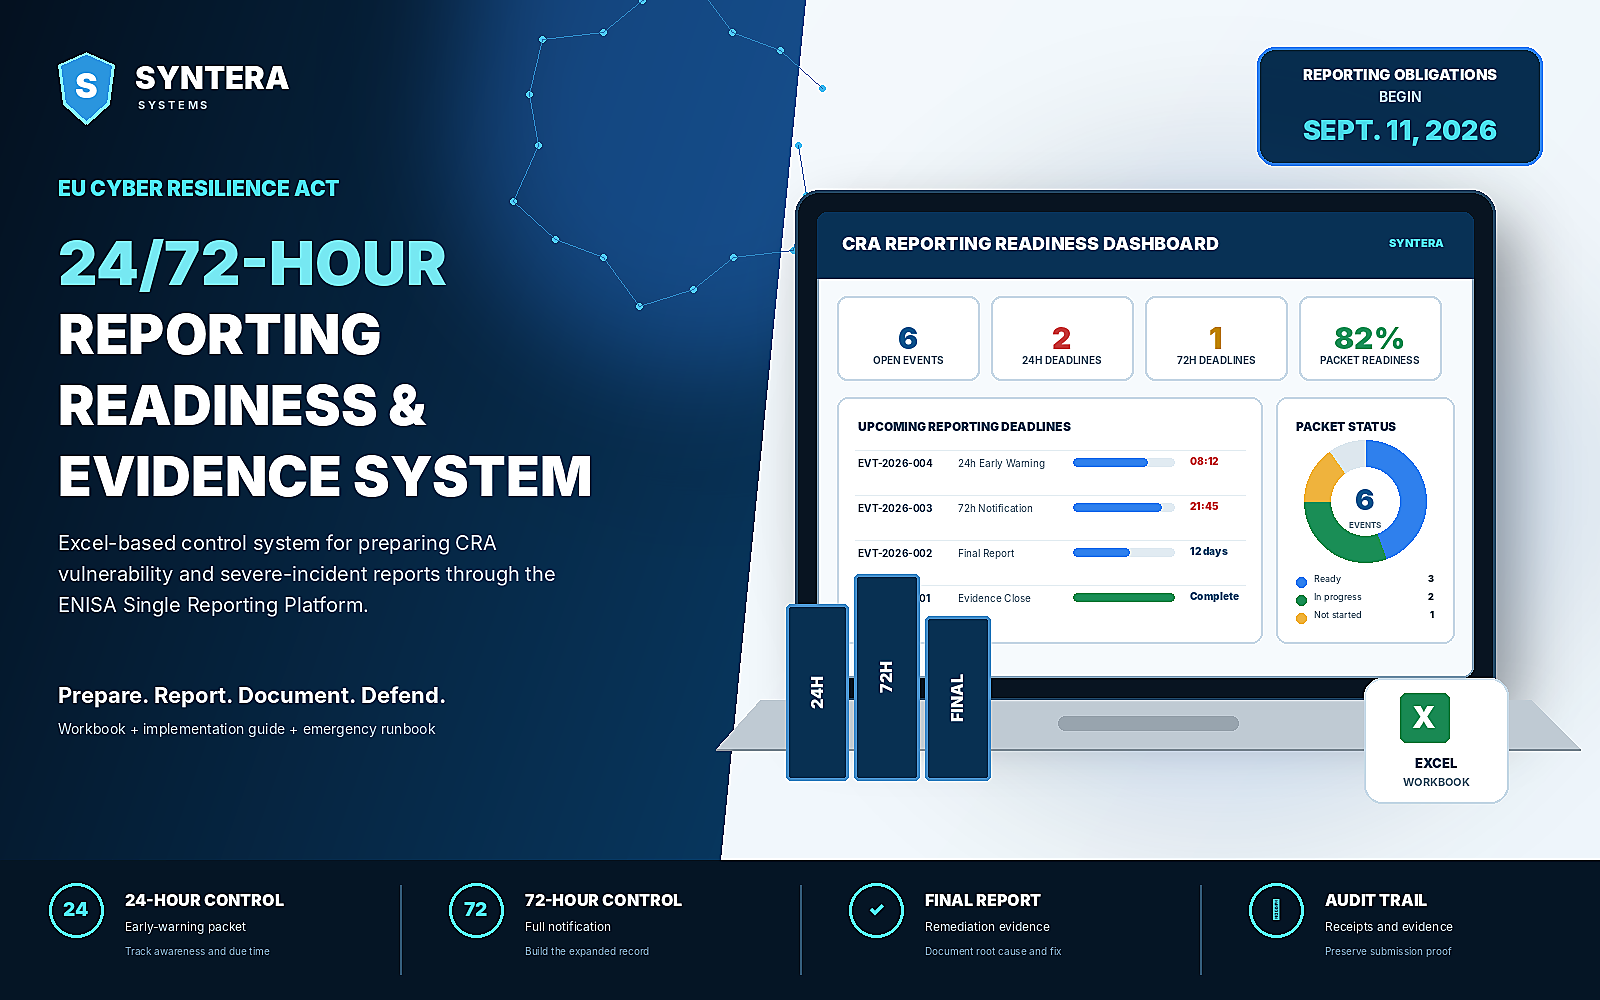
The reporting obligations for actively exploited vulnerabilities and severe incidents having an impact on the security of products with digital elements apply from September 11, 2026. Most other CRA requirements apply later.
Does the workbook submit reports to ENISA?
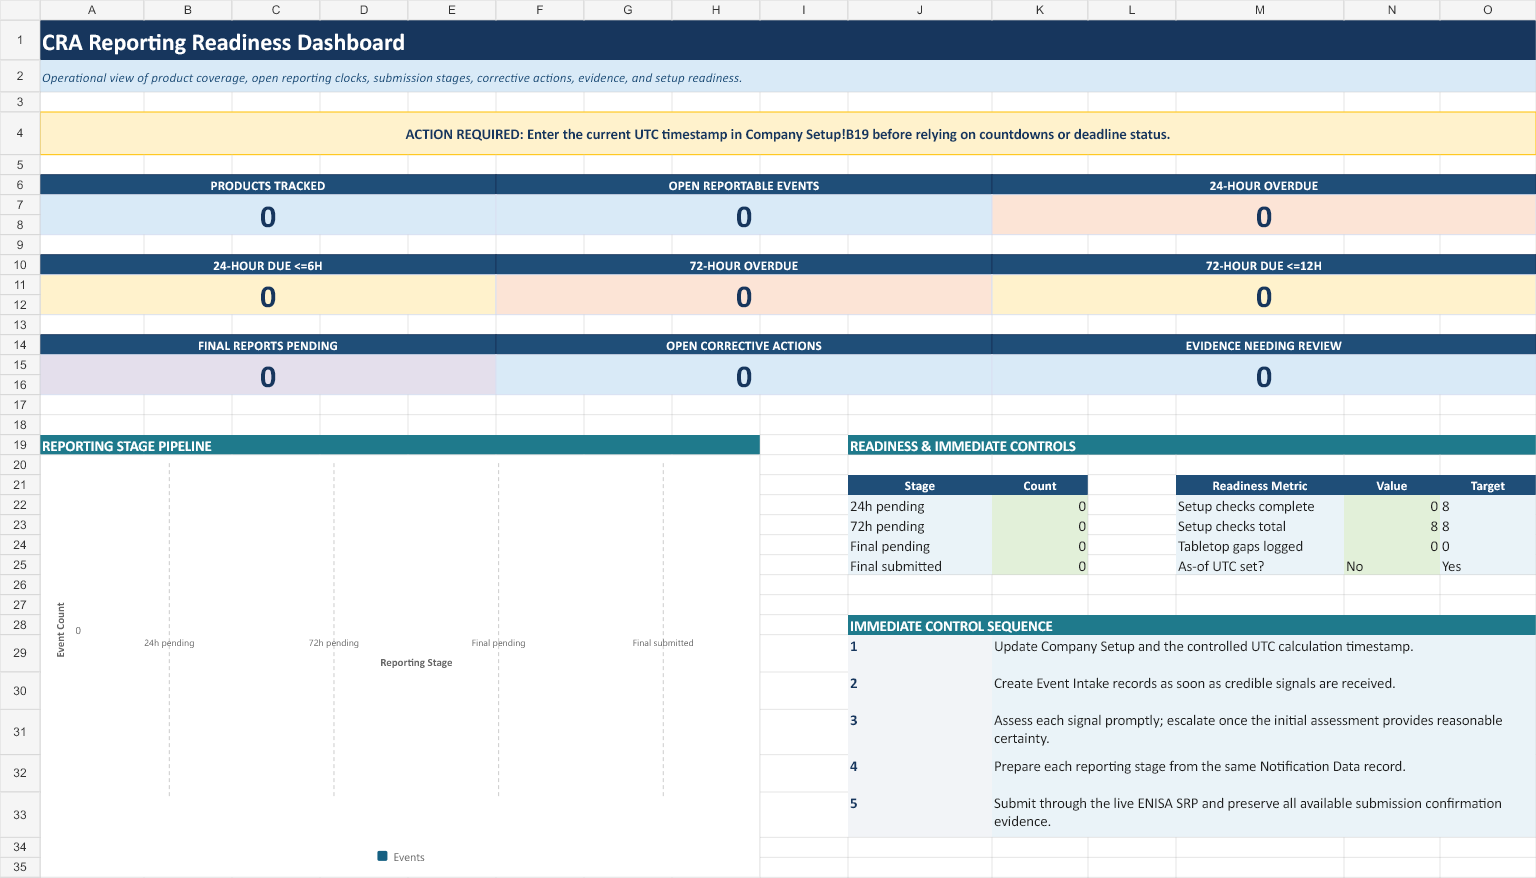
No. It prepares, controls and documents the internal record. Submission remains the manufacturer’s responsibility. ENISA’s “Assigned Representative” is an SRP user role and is distinct from a CRA authorised representative.
What starts the 24-hour reporting clock?
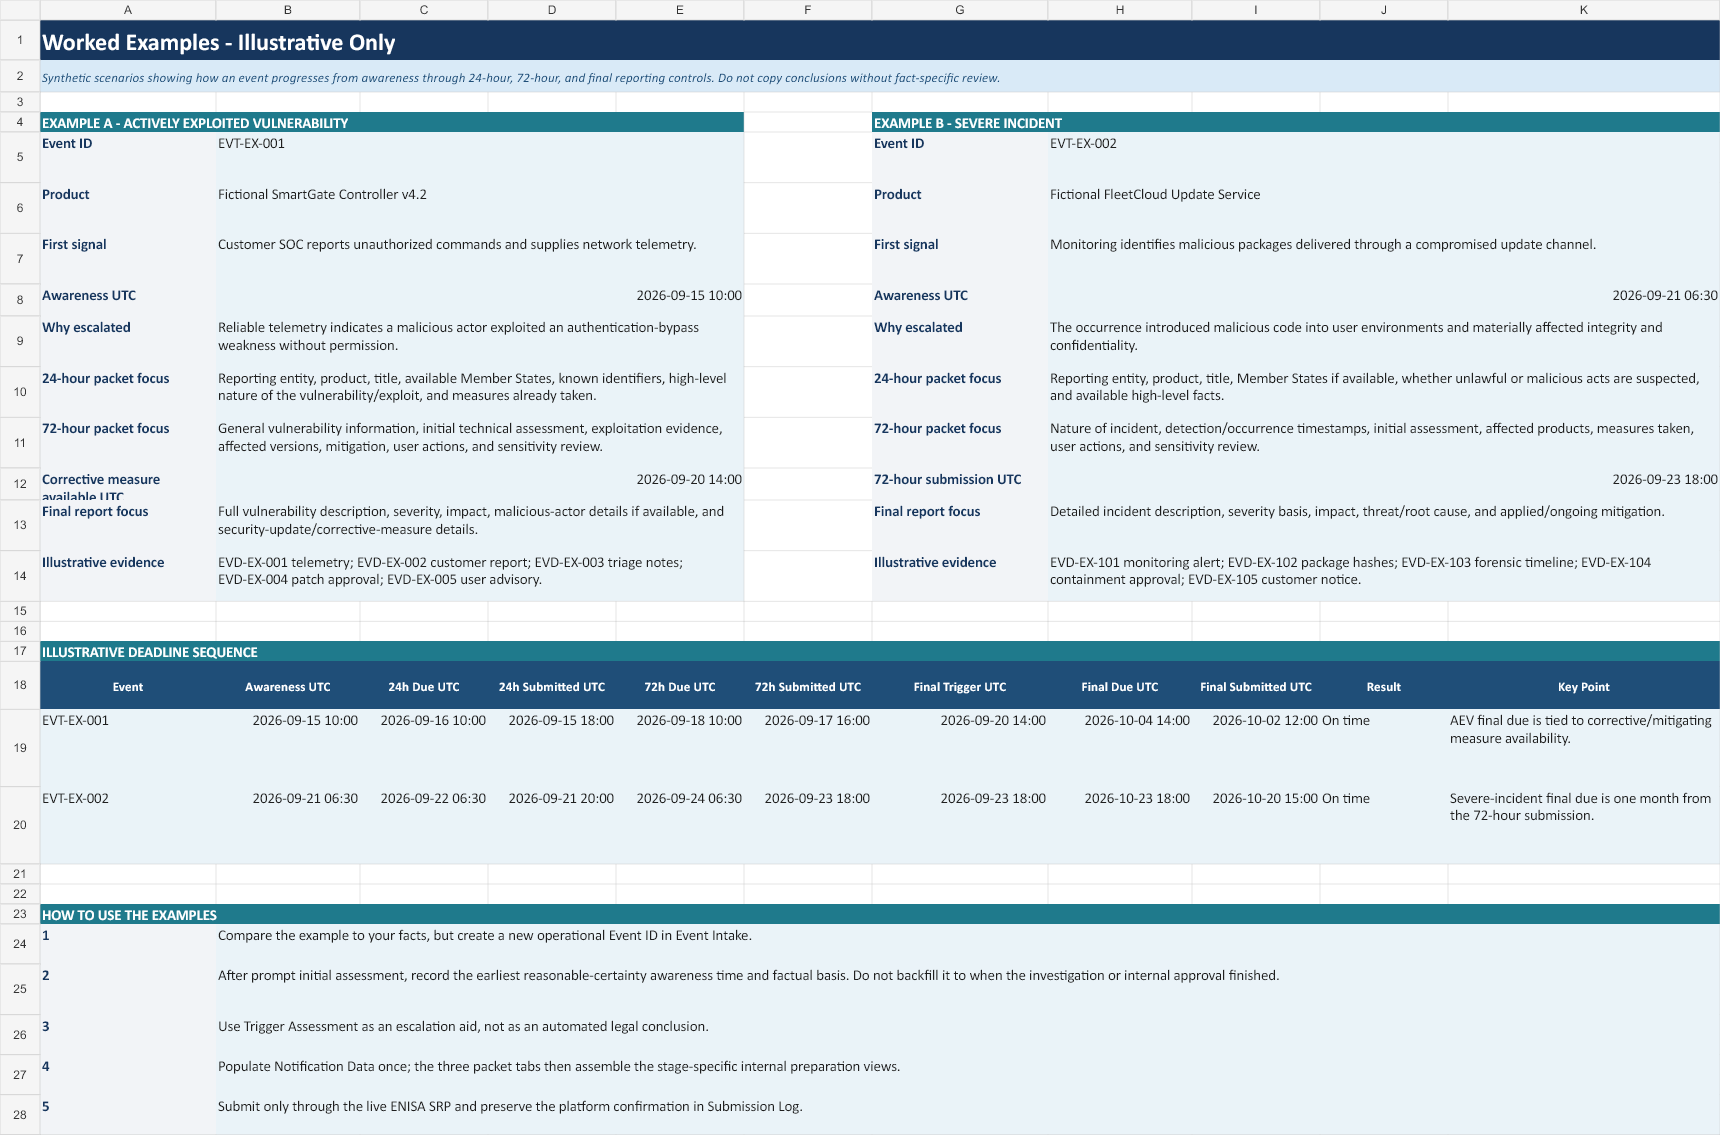
After a prompt initial assessment, awareness is reached when the manufacturer has a reasonable degree of certainty that a reporting trigger is met. A signal alone is not automatically awareness, but internal approval cannot postpone an awareness time already reached.
Is this a complete CRA compliance package?
No. It is limited to reporting readiness and evidence control. It does not replace product cybersecurity engineering, technical documentation, conformity assessment, CE marking, legal advice or incident response.
What does early access include?
The launch package includes the Excel workbook, Quick Guide, First Four Hours Runbook and one post-launch v1.1 alignment update after lawful review. Timing will be announced.
What does the workbook preserve after submission?
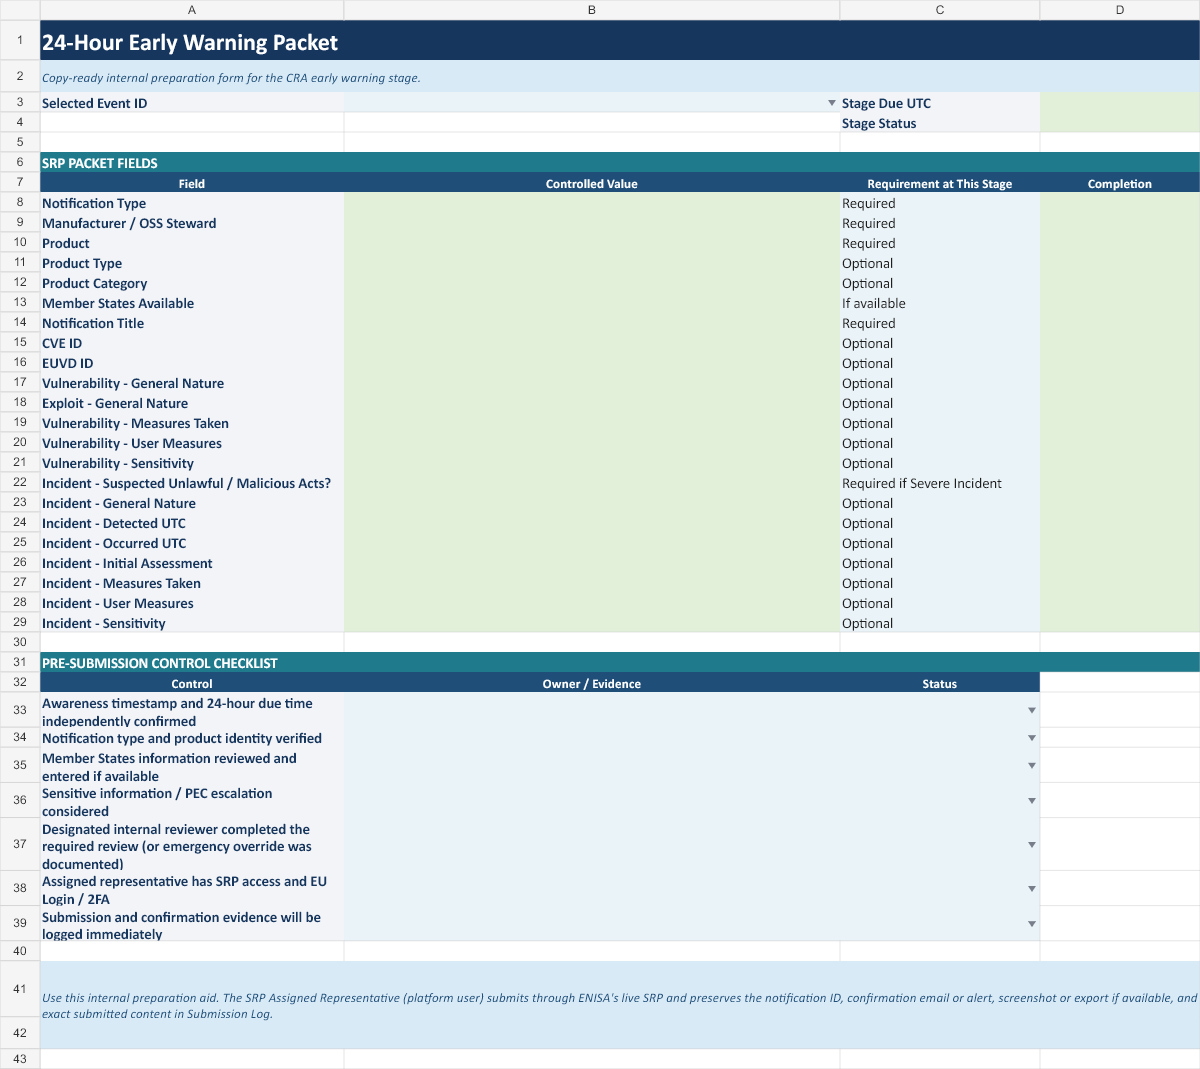
It provides fields for the notification ID, submitter, timestamp, exact stage content, confirmation email or alert, and a screenshot or export if available. ENISA has not documented a separate formal receipt format.
Where are delivery and refund terms shown?
Digital delivery, license and refund eligibility follow the terms displayed on the Payhip checkout and Syntera’s product terms. Product or file questions can be sent to brent@synterasystems.com.
Official sources
- Regulation (EU) 2024/2847 — Cyber Resilience Act
- European Commission — CRA reporting obligations
- ENISA — Single Reporting Platform FAQ
- European Commission — final CRA implementation guidance
Syntera Systems is not affiliated with or endorsed by the European Commission, ENISA or any member-state CSIRT. This product is an operational reporting-readiness and evidence-control aid. It does not determine legal applicability, make a binding reportability decision, provide legal advice, perform incident response or cybersecurity engineering, submit a notification, replace the ENISA platform, complete product technical documentation or certify CRA compliance.